No payment card details, financial or banking information compromised in data breach, says M1
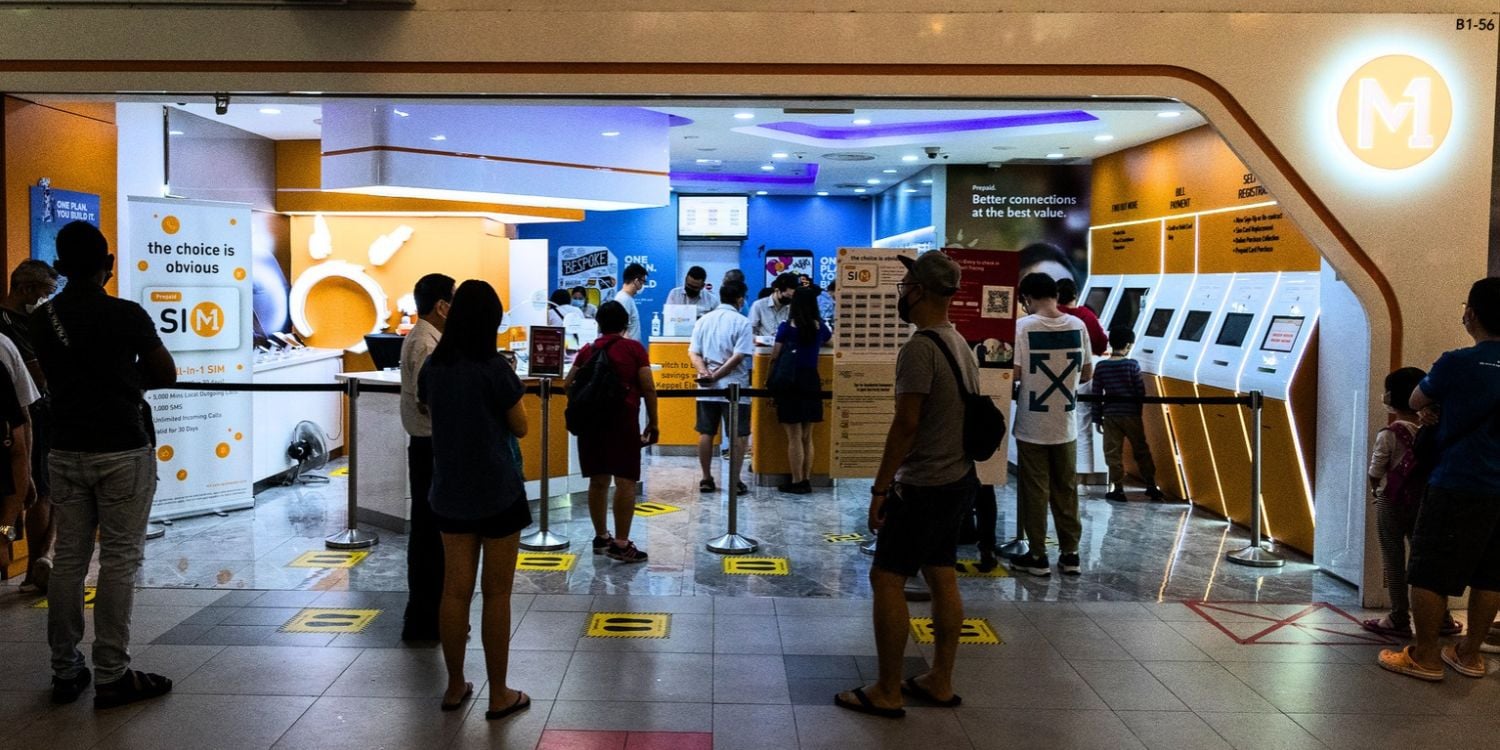
Local telecommunications company M1 has been hit by a data breach, which has since been contained.
However, a certain amount of customers’ personal information was leaked, it said in a news release on Friday (6 Nov).
Customer names & addresses among data affected
The data breach was identified on 30 Oct, M1 said.
The data affected included:
- Customer names
- NRIC/FIN numbers
- Dates of birth
- Mobile numbers
- Email addresses
- Residential addresses
The telco noted that no payment card details, financial or banking information, nor customer account access was compromised.
M1 services fully operational during data breach
M1 maintained that all its services and business operations remained “fully operational” throughout the incident.
Investigations are ongoing, and it has been “working closely” with the relevant authorities and third-party specialists in the probe, it assured, adding:
M1 takes the security and confidentiality of information entrusted to it very seriously.
M1 to reach out to affected customers
While M1 did not specify how many customers were affected, it said it would start reaching out to them via email or post.
It encouraged customers to “remain vigilant and exercise caution” when receiving unsolicited calls, messages or emails.
They should independently verify the identity of those who contact them by getting in touch with the organisation they claim to represent via official channels.
Doctor Anywhere also hit by data breach
M1’s breach was not the only one disclosed on Friday.
Telemedicine provider Doctor Anywhere also said in a statement on Friday night that it had been affected by a data breach, reported The Straits Times (ST).
Source: Google Maps
The company said it became aware on 29 Oct of the “malicious cyber incident”, which involved unauthorised access by an unknown third party.
Customers’ personal data compromised included names, email addresses, identity card (IC) and passport numbers, dates of birth, emergency contact details, and bank account details.
However, it maintained there is “no evidence to suggest” the leakage of passwords, login credentials, payment card details and images of IC documents. All clinical records were also not affected.
Cybersecurity and forensic specialist Ensign InfoSecurity has been engaged, and it has secured the vulnerabilities in the system.
Doctor Anywhere did not specify the number of users affected, but said they are being notified.
Courts fined S$178K for data breach
The two breaches come after electronics and furniture retailer Courts was fined S$178,000 over a massive ransomware attack that led to the personal data of almost one million customers and staff being leaked.
The attack in September 2022 compromised customers’ names, IC numbers, addresses, phone numbers and even the last four digits of their credit card numbers. Current, former and prospective employees had their bank account details and credit information exposed.
This was Courts’ third breach of data protection obligations since January 2019.
Source: Google Maps
In a decision by the Personal Data Protection Commission (PDPC) on 11 Aug that was published by PDPC on 26 Oct, it was held that Courts failed to implement basic cybersecurity policies and practices despite being fined for the two previous breaches.
Thus, a higher financial penalty was warranted the third time round for more effective deterrence, PDPC said.
Other companies to have reported data breaches recently are another telco Simba, personal finance platform MoneySmart and national carrier Singapore Airlines.
PDPC is aware of both M1’s and Doctor Anywhere’s breaches, reported ST.
Also read: MoneySmart CEO Vinod Nair apologises for 29 Oct data breach, some S’pore & Hong Kong users affected
MoneySmart CEO Vinod Nair apologises for 29 Oct data breach, some S’pore & Hong Kong users affected
Have news you must share? Get in touch with us via email at news@mustsharenews.com.
Featured image from MS News.
